

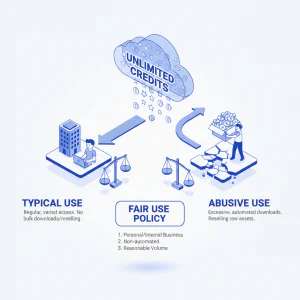
A buyer-grade look at how unlimited credits actually work, what a fair use policy should cover, and how to avoid surprise throttling.
A buyer-grade look at how unlimited credits actually work, what a fair use policy should cover, and how to avoid surprise throttling.
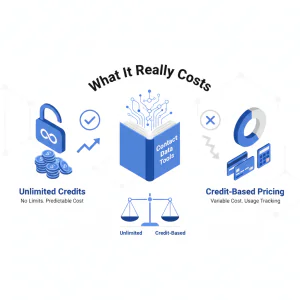
A cynical buyer’s guide to unlimited vs credit-based contact data pricing—hidden costs, data decay, throttling, and cost per connect.
Submit a privacy opt-out request to remove your data from Swordfish. Steps, CCPA/GDPR guidance, and what durable suppression looks like.
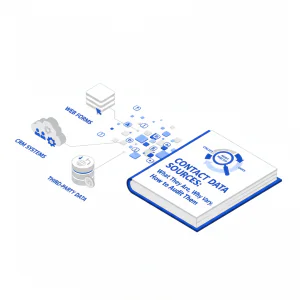
A buyer’s breakdown of contact data sources for healthcare provider outreach: first-party, third-party, public registries, decay, and opt-out audits.
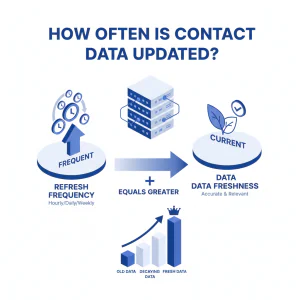
A cynical buyer’s guide to contact data refresh claims: why they hide decay, what recency signals to require, and how to test freshness yourself.
A buyer-grade security audit guide for contact data tools: access controls, audit logs, encryption, vendor risk, retention, and when to stop the evaluation.
A buyer/auditor look at Swordfish’s Chrome extension for contact data: workflow fit, permissions, data decay, fair-use limits, and a pilot test plan.
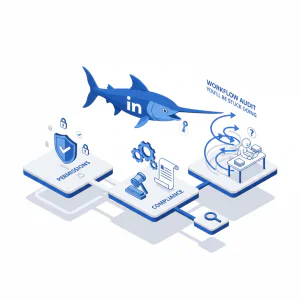
A buyer’s audit guide to the Swordfish LinkedIn extension: permissions, compliance, workflow reliability, exports, data decay, and pilot testing.
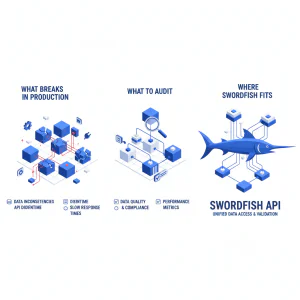
A buyer’s guide to evaluating a contact data API: what breaks under rate limits, how provider data decays, and how to test Swordfish before you commit.
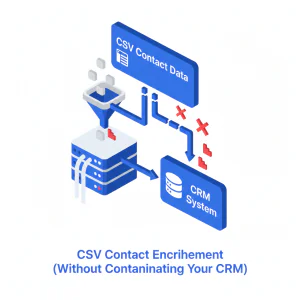
A governance-first CSV enrichment workflow: fix dirty data, dedupe contacts, validate identity columns, and import into Salesforce or HubSpot cleanly.
Talk to our data specialists to get started with a customized free trial.